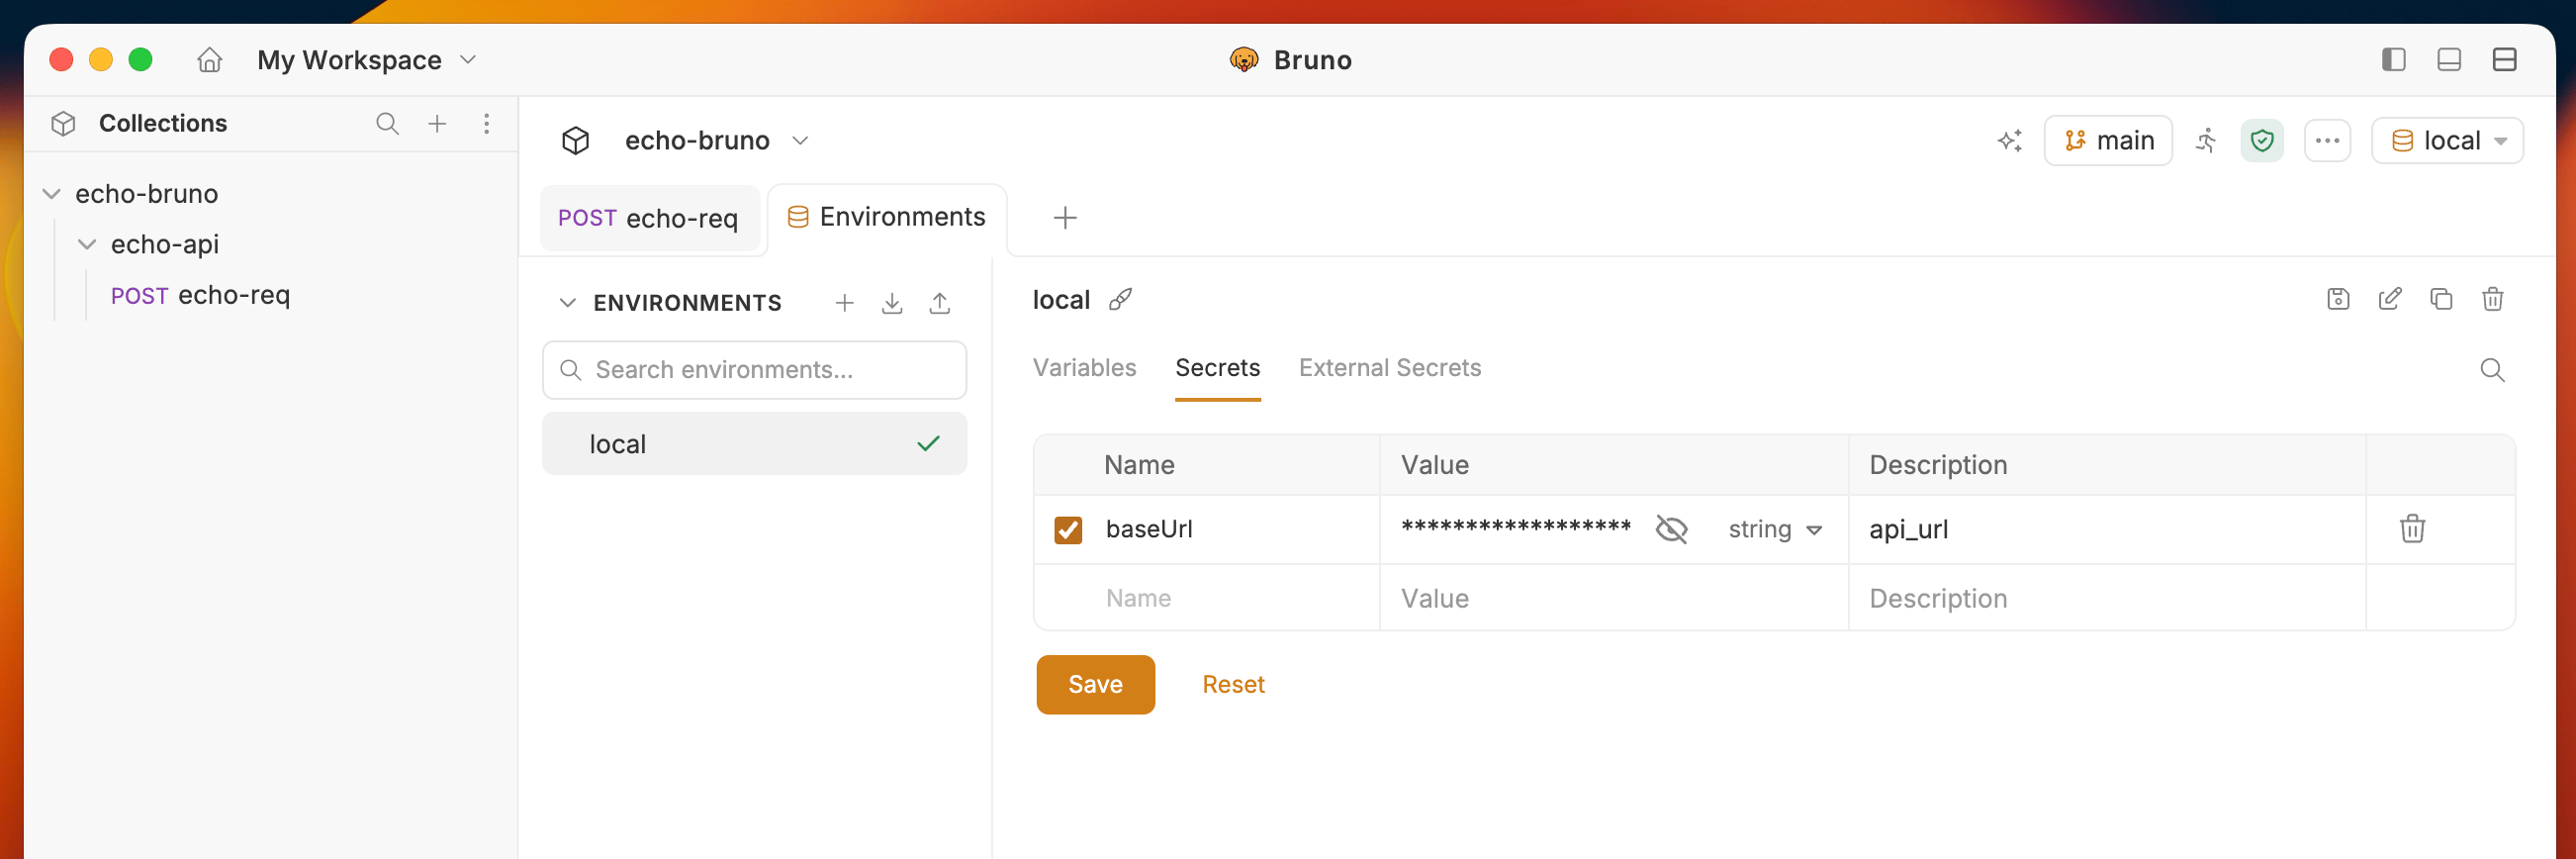
Bruno stores secrets on your local machine. The location depends on the OS.
The secrets are encrypted using OS level encryption when available or falls back to AES256 encryption.
Secret variables are special variables that are used to store sensitive information such as API keys, passwords, tokens, etc.Bruno provides a separate tab for secret variables to avoid confusion between normal and secret vars. You can access secret variables tab by navigating to specific environment and clicking on the Secrets tab.Your environment file stores only the secret name (and optional metadata). The secret value stays in Bruno’s local encrypted store, not in the file.For OpenCollection YAML environments (environments/dev.yml):
name: devvariables: - secret: true name: apiKey description: "API key for the API"
Starting from v4.0.0, all secret variables are displayed in a separate tab to avoid confusion between normal and secret vars. Secret values are stored securely and are not saved to the environment file.
You can safely check your collection into source control without exposing secrets.When you export your collection as a file, Bruno will not export the secret variable values.