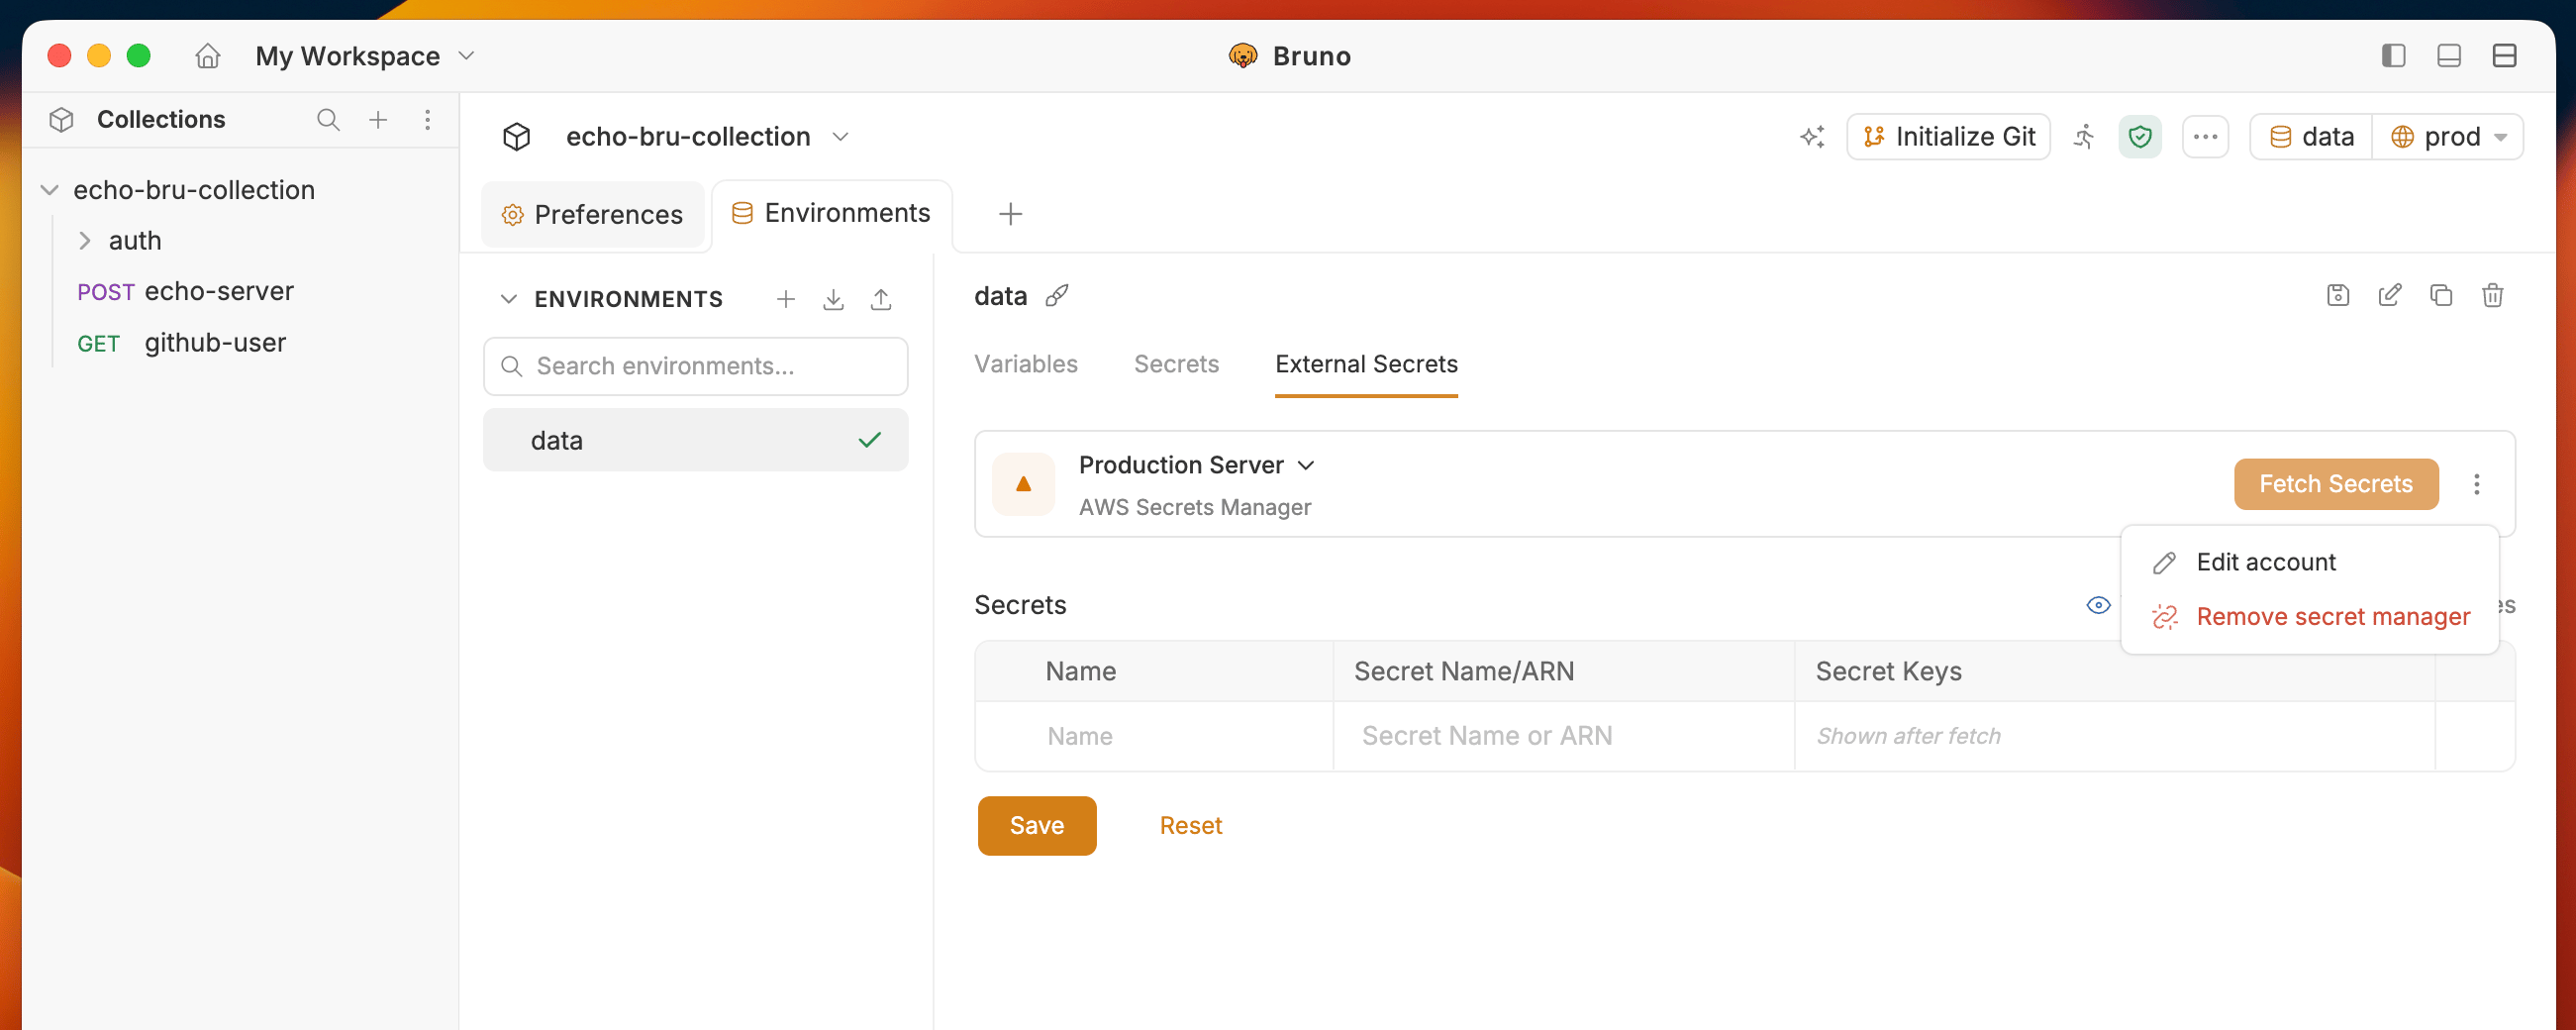
Starting from Bruno v4.0.0, secret manager configuration has moved from Collection > Secrets to Environment > External Secrets.
Fetching and storage
- Fetch Secrets loads values into a per-environment, in-memory cache for the session only.
- Secret values are never written to disk — only provider config and identifiers are saved.
- Closing the app or collection clears the cache. Reopen Bruno and it will fetch secrets on demand.
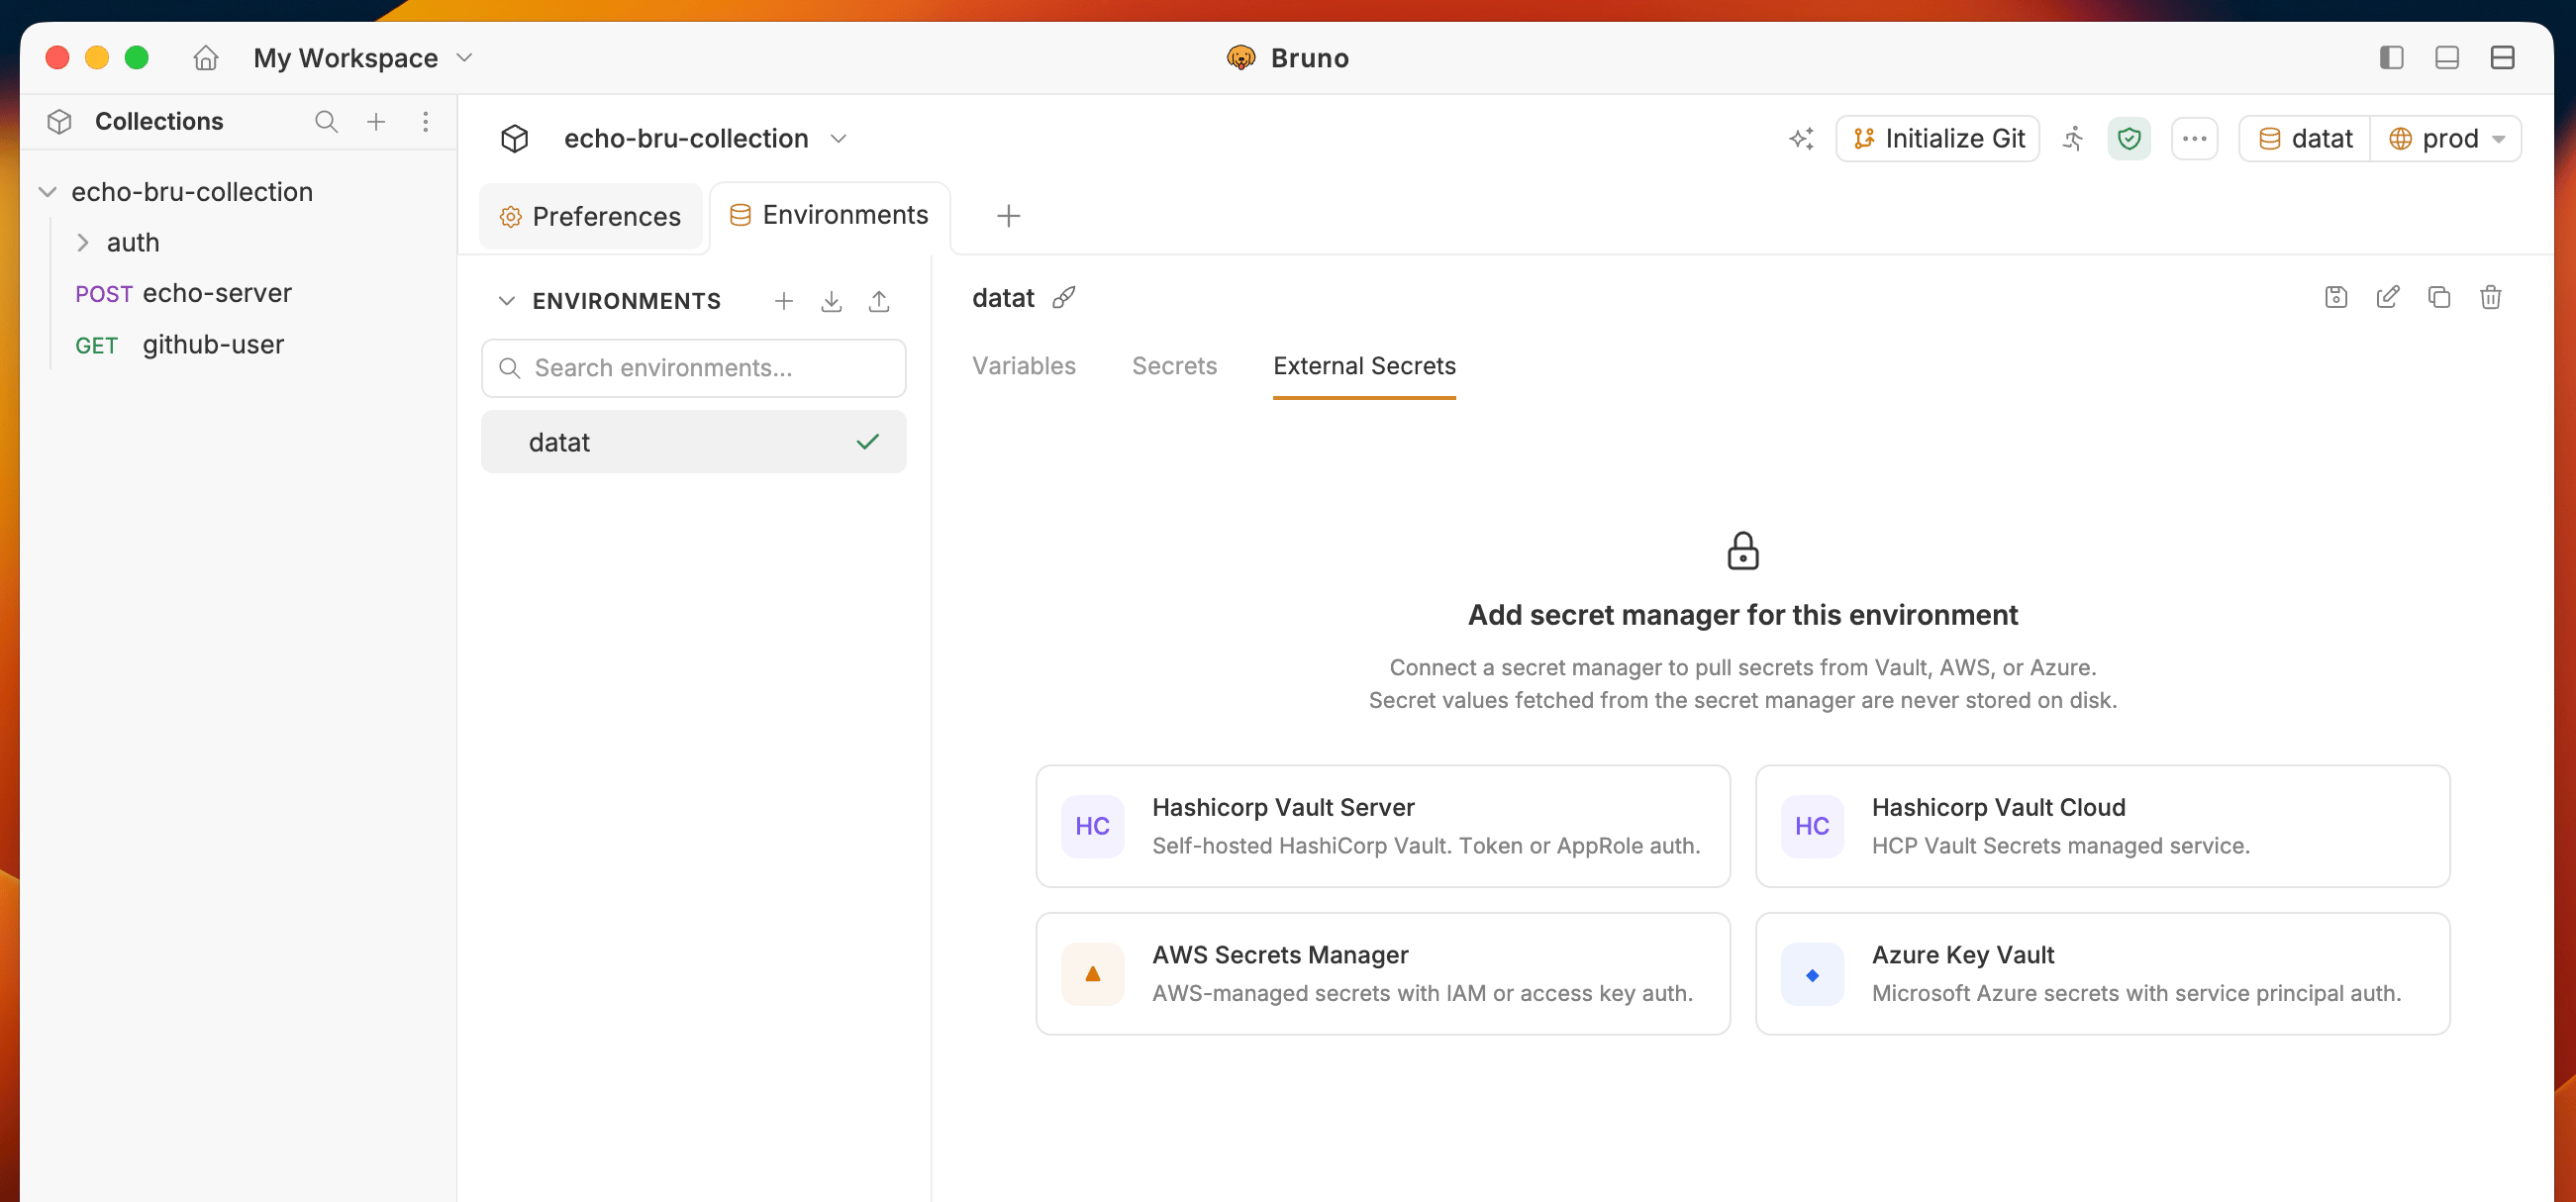
- Go to Environment > External Secrets and select AWS Secrets Manager
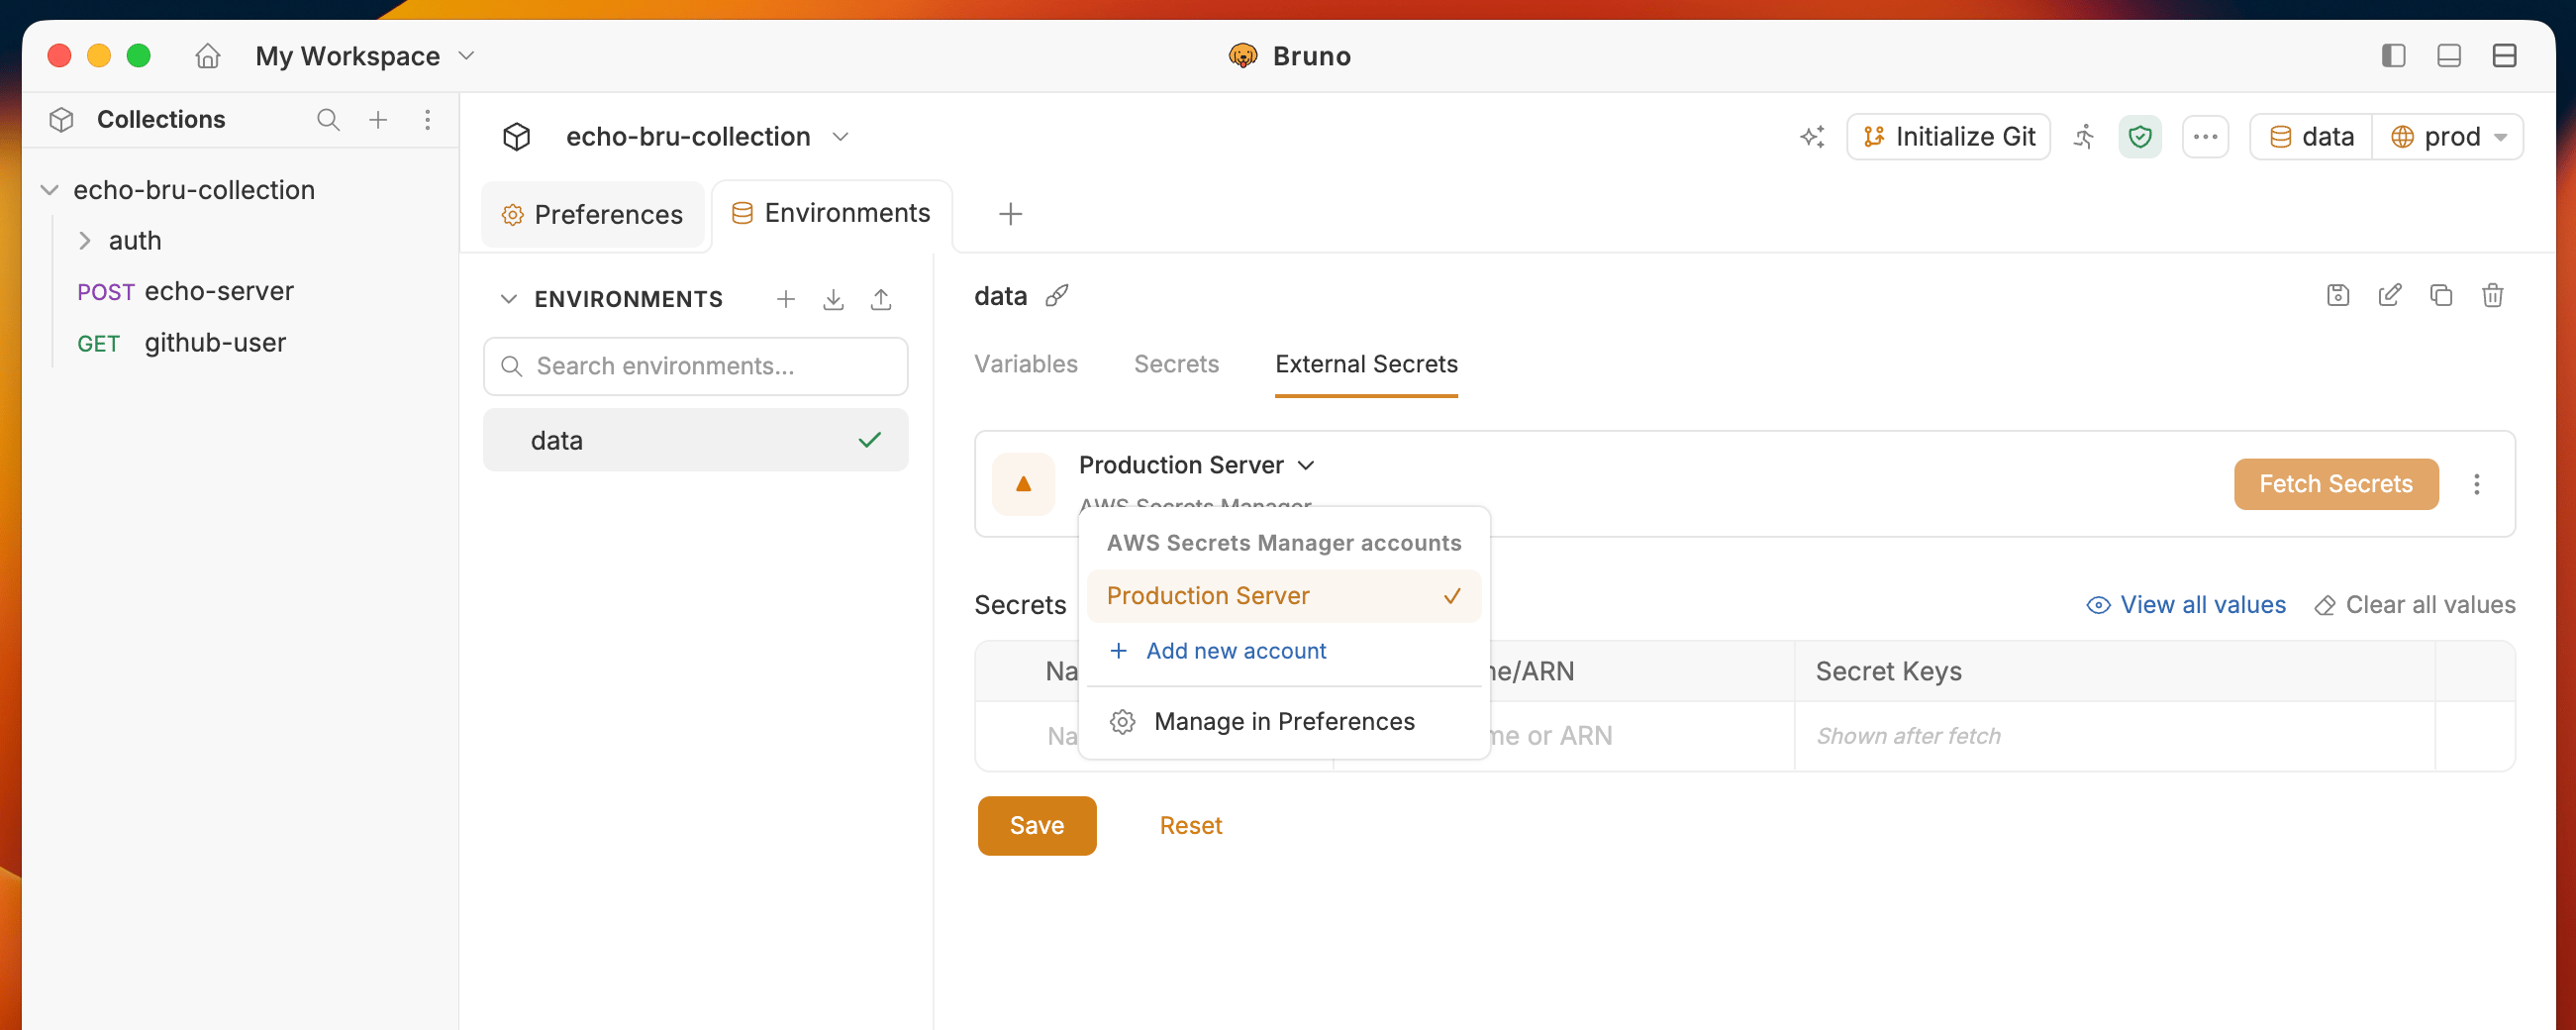
- You will see the configured Secret Manager accounts list from Preferences settings. Select the AWS Secrets Manager account you want to use.
- Use Add new account button to add a new AWS Secrets Manager account
-
Enter a Name and the AWS Secret Name or ARN for the secret you want to fetch.
- Name - the alias used to reference the secret in Bruno, e.g.
apiCredentials - AWS Secret Name / ARN - the exact secret name or full ARN, e.g.
prod/api-keyorarn:aws:secretsmanager:us-east-1:123456789012:secret:prod/api-key
- Name - the alias used to reference the secret in Bruno, e.g.
- Click the Fetch Secrets button in the top-right corner.
- Fetched secret keys appear under Secret Keys. Values stay in the in-memory session cache and are not persisted to disk.
- Edit account to edit the account details
- Remove secret manager to remove the secret manager configuration